Applicant tracking systems and career portals have become prime targets for sophisticated AI-driven fraud rings. Recent industry analysis indicates that resume parsing attacks have increased by over 400% in the last three years, forcing enterprise employers to rethink their security protocols. This surge in automated deception threatens not only data integrity but also the fairness of hiring processes for millions of candidates worldwide. Organizations must adopt proactive defense mechanisms to protect their recruitment infrastructure from these evolving threats. (Contact Us)
The Rise of AI Fraud in Recruitment
The landscape of digital recruitment has shifted dramatically with the advent of generative artificial intelligence. Fraudsters now utilize large language models to create convincing fake resumes, generate synthetic identities, and automate application submissions at scale. According to a 2024 report by the Identity Theft Resource Center, identity-related fraud in hiring processes has reached unprecedented levels, costing employers billions in wasted resources and compliance risks. This trend highlights the urgent need for robust verification systems that can distinguish between genuine candidates and automated threats.
Traditional security measures often fail against these advanced tactics because they rely on static rules that can be easily bypassed. For instance, simple CAPTCHA systems can be defeated by AI-driven solving services that mimic human behavior with high accuracy. Employers must therefore implement dynamic, behavior-based security solutions that analyze user interactions in real-time. This approach allows organizations to detect anomalies that static filters miss, ensuring a safer environment for legitimate applicants.
Case Study 1: Automated Bot Infiltration
One of the most common forms of AI fraud involves the use of automated bots to flood career sites with fake applications. These bots are designed to scrape job postings and submit thousands of generic resumes within minutes. In a notable incident involving a major tech firm, over 10,000 fraudulent applications were detected in a single week, all originating from IP addresses associated with known bot networks. The sheer volume of these submissions overwhelmed human recruiters and skewed performance metrics for legitimate candidates.
Match2 addressed this threat by implementing advanced behavioral analysis tools that monitor mouse movements, typing patterns, and session duration. By analyzing these micro-behaviors, the system can identify non-human interactions with high precision. This method proved effective in blocking the majority of bot traffic, allowing recruiters to focus on high-quality candidates. The result was a significant reduction in processing time and an improvement in the overall candidate experience.
Case Study 2: Deepfake Identity Verification
As video interviews become more prevalent, deepfake technology has emerged as a new vector for fraud. Fraudsters use AI-generated video overlays to impersonate candidates during live interviews, bypassing identity verification checks. A recent case highlighted in a 2025 cybersecurity journal described a scenario where a candidate used real-time deepfake software to mimic their own face during a video screening. This allowed them to pass initial identity checks despite using a stolen identity for the application.
To combat this, Match2 integrated liveness detection protocols that require candidates to perform random, spontaneous actions during video verification. These actions, such as turning their head or blinking in a specific pattern, are difficult for current deepfake algorithms to replicate in real-time. This layer of security ensures that the person interacting with the system is indeed the applicant. It also provides a robust defense against pre-recorded video attacks that might otherwise bypass simpler verification methods.
Case Study 3: Credential Stuffing Attacks
Credential stuffing involves using stolen login credentials from other breaches to access career site accounts. Attackers automate this process to gain unauthorized access to candidate profiles, often to steal personal data or manipulate application statuses. Data from the Verizon Data Breach Investigations Report shows that credential stuffing remains one of the top causes of account takeover incidents in the recruitment sector. This type of attack is particularly dangerous because it exploits the reuse of passwords across multiple platforms.
Match2 mitigates this risk by enforcing strict multi-factor authentication (MFA) policies for all user accounts. Additionally, the platform monitors for suspicious login patterns, such as logins from unusual geographic locations or devices. When such anomalies are detected, the system automatically triggers additional verification steps or temporarily locks the account. This proactive approach prevents unauthorized access and protects sensitive candidate information from being compromised.
Match2 Defense Strategies
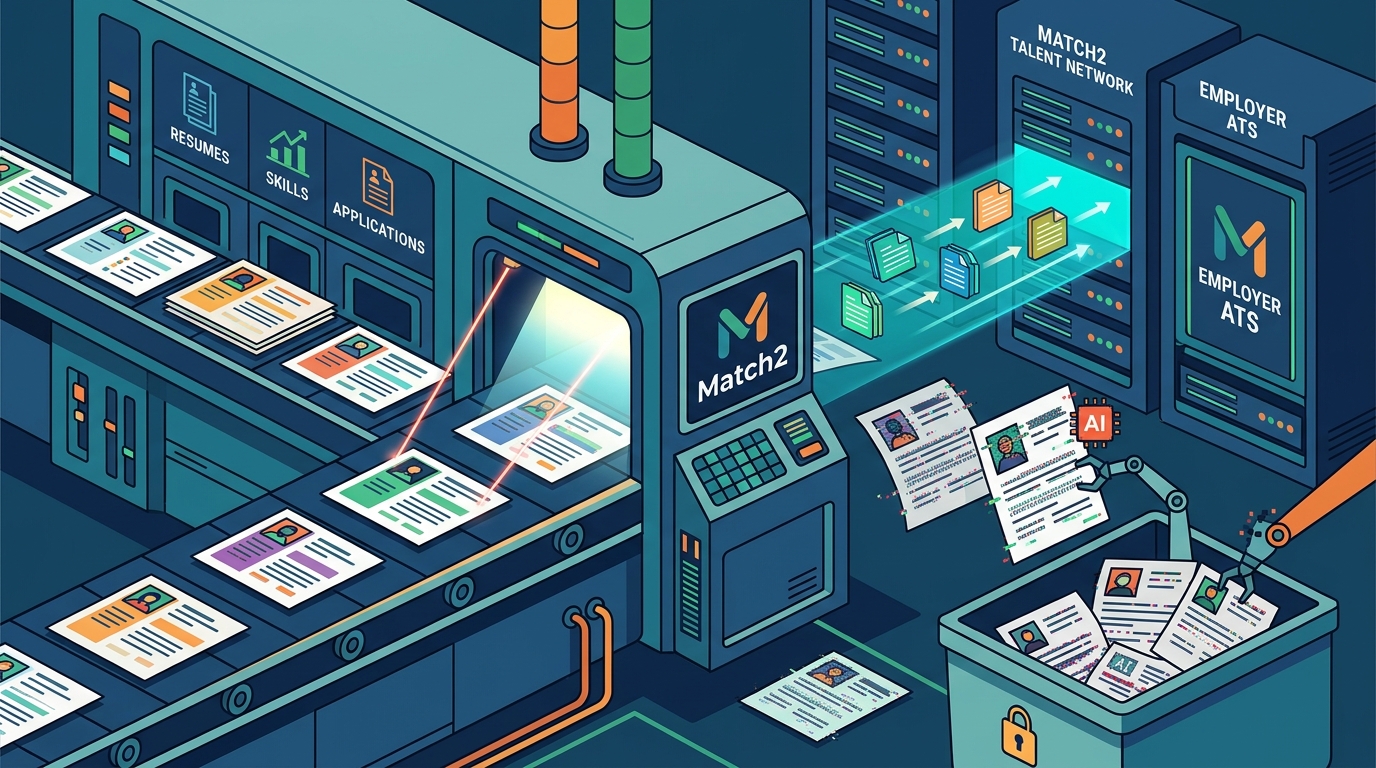
Match2 employs a multi-layered security architecture designed to address the full spectrum of AI-driven threats. The core of this strategy involves continuous monitoring and adaptive response mechanisms that evolve alongside emerging attack vectors. By leveraging machine learning algorithms, the system can identify new patterns of fraud that have not been previously encountered. This adaptive capability ensures that defenses remain effective against novel threats.
Another critical component is the integration of third-party threat intelligence feeds. These feeds provide real-time data on known malicious IP addresses, domains, and behavioral signatures. By cross-referencing this data with incoming traffic, Match2 can block threats before they reach the application layer. This proactive stance significantly reduces the attack surface and enhances the overall security posture of the career site.
Behavioral Biometrics
Behavioral biometrics analyze unique user characteristics such as typing speed, mouse pressure, and navigation habits. These metrics are difficult to replicate by bots or impersonators, making them a reliable indicator of authenticity. Match2 uses these insights to create a unique fingerprint for each user, which is continuously updated to reflect changes in behavior. This dynamic profiling allows for seamless authentication without requiring constant user intervention.
Real-Time Risk Scoring
Every interaction on the career site is assigned a real-time risk score based on multiple factors. These factors include device reputation, location data, and behavioral anomalies. If the risk score exceeds a predefined threshold, the system triggers additional verification steps or blocks the action entirely. This granular approach ensures that legitimate users are not unduly hindered while maintaining strict security controls.
Automated Response Workflows
In the event of a detected threat, Match2 automates the response workflow to minimize manual intervention. This includes isolating suspicious accounts, notifying security teams, and updating threat intelligence databases. Automation ensures that responses are immediate and consistent, reducing the window of opportunity for attackers. It also frees up security personnel to focus on more complex investigative tasks.
Key Takeaways
- AI-driven fraud in recruitment has increased by over 400% in recent years, necessitating advanced defense mechanisms.
- Automated bot infiltration can overwhelm recruitment systems, as seen in cases with thousands of fake applications.
- Deepfake technology poses a significant risk to video-based identity verification processes.
- Credential stuffing remains a primary cause of account takeover incidents in the hiring sector.
- Match2 utilizes behavioral biometrics to create unique user fingerprints for enhanced security.
- Real-time risk scoring allows for dynamic response to potential threats based on multiple data points.
- Integration with third-party threat intelligence feeds provides proactive protection against known malicious actors.
Frequently Asked Questions
How does Match2 detect AI-generated fake resumes?
Match2 employs natural language processing algorithms to analyze the structure and content of submitted resumes. These algorithms look for patterns typical of AI-generated text, such as overly generic phrasing or inconsistent formatting. Additionally, the system cross-references resume data with external databases to verify employment history and educational credentials.
What is behavioral biometrics and how is it used?
Behavioral biometrics refers to the analysis of unique user behaviors such as typing rhythm and mouse movements. Match2 uses this data to create a dynamic profile for each user. If the behavior deviates significantly from the established profile, the system flags the interaction for further review.
Can deepfake technology bypass video verification?
While deepfake technology is advancing rapidly, Match2's liveness detection protocols are designed to counter these threats. By requiring random, spontaneous actions during video verification, the system can identify inconsistencies that deepfakes cannot replicate in real-time.
How does Match2 protect against credential stuffing?
Match2 enforces multi-factor authentication and monitors for suspicious login patterns. If a login attempt originates from an unusual location or device, the system triggers additional verification steps to confirm the user's identity.
What role does threat intelligence play in Match2's security?
Threat intelligence feeds provide real-time data on known malicious actors and attack vectors. Match2 uses this information to proactively block threats before they reach the application layer, enhancing the overall security of the career site.
Is Match2's security solution customizable for different industries?
Yes, Match2 offers customizable security modules that can be tailored to the specific needs of different industries. This includes adjusting risk thresholds, configuring verification steps, and integrating with existing HR systems.
How often are Match2's security protocols updated?
Match2 continuously updates its security protocols to address emerging threats. This includes regular software patches, algorithm updates, and integration of new threat intelligence data to ensure optimal protection.
What happens if a threat is detected on a Match2 career site?
When a threat is detected, Match2's automated response workflows are triggered. This includes isolating suspicious accounts, notifying security teams, and updating threat databases. The goal is to mitigate the threat immediately and prevent further damage.
Secure Your Career Site Today
Protecting your recruitment infrastructure from AI-driven fraud is no longer optional. As threats evolve, so must your defenses. Match2 provides comprehensive security solutions tailored to the unique challenges of modern hiring. Visit our Security Solutions page to learn more about our offerings. Contact our team to schedule a demo and see how we can safeguard your career site. Explore our Career Site Best Practices guide for additional insights. Join the many organizations that trust Match2 for secure and efficient recruitment. Discover our About Us page to learn more about our mission and values.